Is Kiss918 a scam? The main security risk is often not the brand itself, but fake APK files, phishing pages, impersonator agents and Telegram prediction-bot scams using familiar branding.
This guide shows Malaysian users how to recognise suspicious downloads, verify a Kiss918 installation, inspect Android permissions and avoid common mobile-gambling scams.
Security Alert
Do not install an APK received unexpectedly through Telegram, WhatsApp, TikTok or another private message. A modified Android package can display the expected login screen while running malicious code in the background.
kiss918.games is an independent review and security-information resource. We monitor suspicious distribution methods and scam patterns associated with the platform and its name.
Is Kiss918 a Scam or Are There Fake Versions?
A logo, filename or familiar login screen does not prove that a download is genuine.
Scammers can imitate the visual identity of a gaming platform and distribute their own Android package, redirect users through a phishing landing page or impersonate an agent through social media.
Most security complaints fall into a few clear categories:
- modified or fake APK files;
- fraudulent Telegram channels;
- unofficial WhatsApp agents;
- cloned login pages;
- fake app updates;
- “RTP hack” and prediction-bot offers;
- suspicious payment instructions.
Key point: Technical app safety and operator trustworthiness are not the same thing. An APK can be malware-free while the agent handling a payment is still untrustworthy.
Latest Scam Alerts in Malaysia
The table below summarises the main patterns users should recognise before installing an app or sending money.
| Threat | Typical Lure | Main Risk | Severity |
|---|---|---|---|
| Fake Telegram channels | “100% win bot”, “free credit”, “VIP prediction” | Phishing, fake deposits, malicious downloads | Critical |
| Modified APK files | “Latest version”, “Malaysia MOD”, “anti-ban APK” | Credential theft, spyware, Trojan-Banker behaviour | Critical |
| Unofficial agents | “Special bonus”, “private bank account” | Deposit theft or withdrawal disputes | High |
| Prediction / hack bots | “RTP scanner”, “AI jackpot predictor” | Advance-fee fraud or malware | Critical |
| Fake update pages | “App expired”, “certificate update required” | Repacked APK or unsafe device profile | High |
File-size warning: An expected APK size can help identify an obvious anomaly, but file size is NOT a guaranteed safety indicator. Attackers can add padding or other data to make a malicious package match an expected size.
Fake Kiss918 Telegram Channels & Prediction Bots
One common scam starts with a Telegram channel promoting claims such as:
- “100% win prediction”
- “private RTP scanner”
- “AI jackpot signals”
- “free credit without deposit”
- “VIP algorithm access”
Large subscriber numbers do not prove legitimacy. Followers, reactions and testimonials can all be manipulated.
The channel may eventually send the user to a fake registration page, unknown APK or payment account controlled by the scammer.
Fake 918Kiss APK & Trojan-Banker Risk
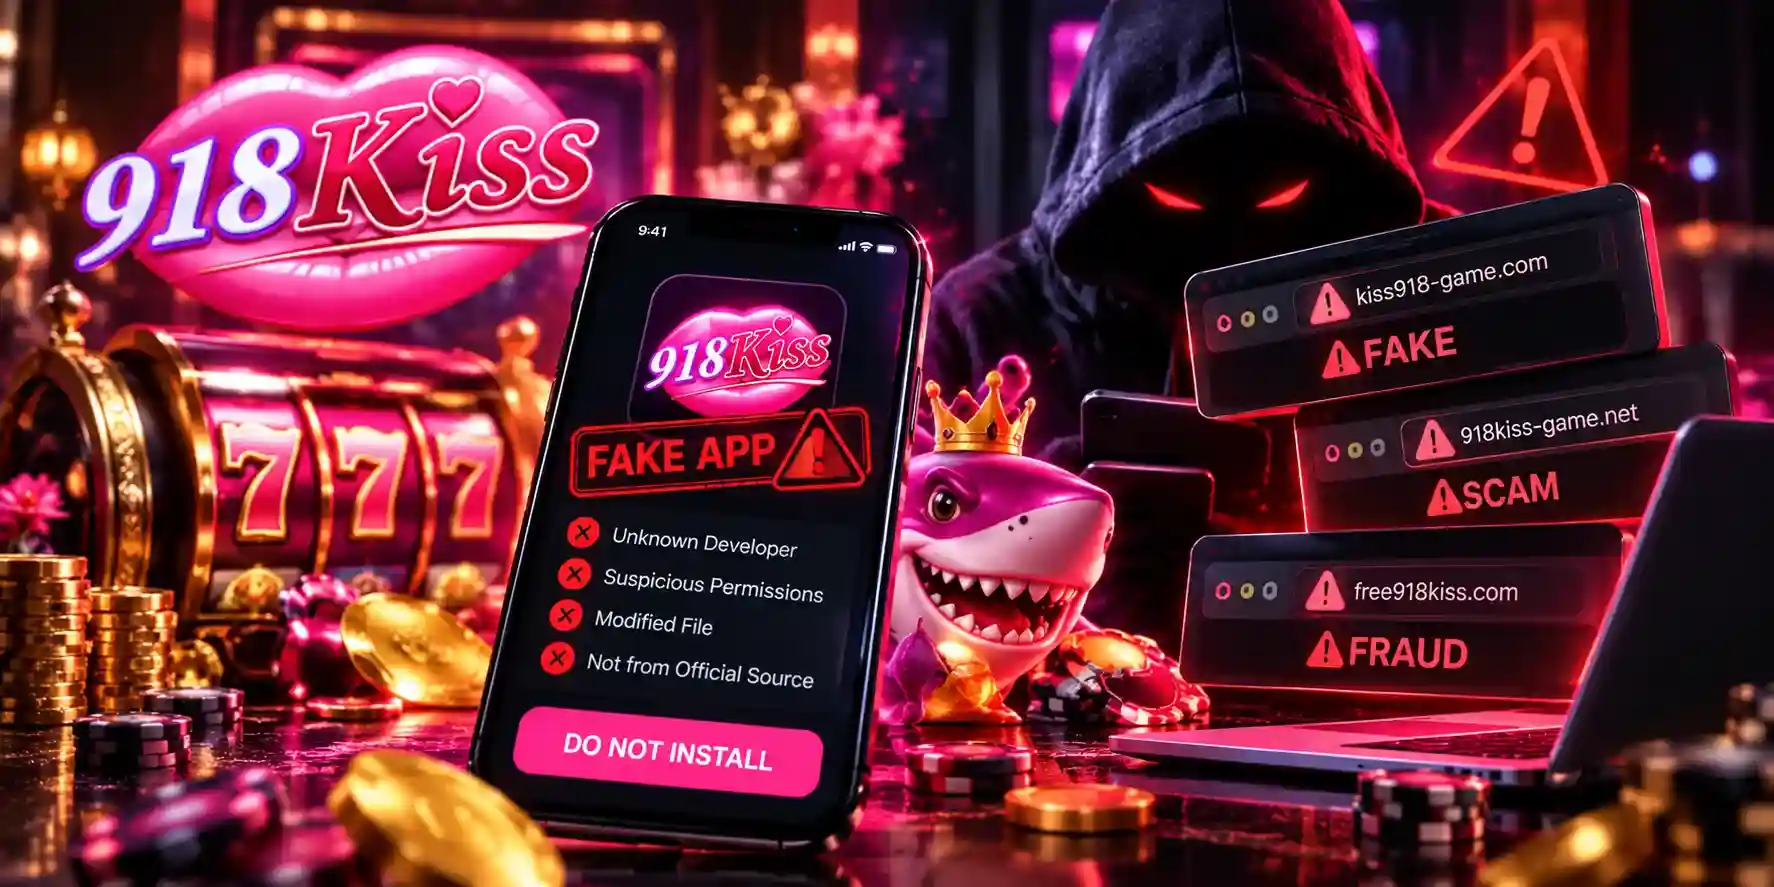
A fake 918Kiss APK may reuse the expected icon, name and login interface while containing additional code.
Depending on the malware family, a malicious gaming app may attempt to:
- read notifications;
- capture login credentials;
- abuse Accessibility Services;
- display overlays above banking apps;
- monitor SMS messages;
- redirect the browser;
- download additional payloads.
Security researchers often describe financially motivated Android malware with these behaviours as Trojan-Banker malware.
The visual appearance of an app therefore provides almost no meaningful proof of authenticity.
Unofficial WhatsApp Agents & Fake Payment Requests
Fraud does not always involve malware.
An impersonator may contact players through WhatsApp and offer:
- unusually large bonuses;
- faster withdrawals;
- a “VIP account”;
- private payment details;
- a new bank account for deposits.
Treat unexpected changes in payment instructions as a warning sign.
How to Verify a Kiss918 APK Before Installation
A proper security check uses several independent signals. Do not rely on filename, icon or file size alone.
1. Verify the APK Download Source
Start by asking where the file actually came from.
Higher-risk sources include:
- Telegram file attachments;
- WhatsApp messages;
- TikTok or Facebook DMs;
- shortened URLs;
- anonymous file-hosting sites;
- “MOD APK” directories;
- unknown mirror domains.
A filename such as:
kiss918-official.apk
or:
918kiss-latest.apk
does not prove anything. Android filenames can be changed without altering the application itself.
Use our app installation page as the starting point for current Android and iOS instructions.
2. Compare the APK File Size
The Android build commonly used as a reference is approximately 45 MB, although package size can change between releases.
A file that is dramatically smaller or larger than the expected version deserves additional investigation.
For example:
| Check | Result |
|---|---|
| Close to expected build size | Useful as a basic consistency check |
| Under ~15 MB | Investigate before installation |
| Over ~100 MB | Investigate before installation |
| Exactly the expected size | Still not proof of safety |
Size can be faked.
Malware authors can use padding, embedded assets or additional code to make a malicious package approximately the same size as a genuine build.
File size should therefore be treated as an anomaly signal, not authentication.
3. Inspect Android Manifest Permissions
Android applications declare requested capabilities through their Android Manifest permissions.
After installation, review:
Settings → Apps → Kiss918 / 918Kiss → Permissions
Be particularly cautious if a gaming client requests:
- SMS access;
- contacts;
- call logs;
- Accessibility Services;
- Device Administrator;
- notification access;
- overlay permissions;
- microphone access without a clear feature;
- precise location without a clear reason.
Permissions such as READ_SMS, READ_CONTACTS or powerful Accessibility access should not be required merely to play a slot game.
Critical Red Flag
If an app claims that SMS or Accessibility access is required to “unlock RTP”, activate bonuses or improve winning chances, stop using it.
4. Do Not Use a Google Play Protect Bypass
Keep Google Play Protect enabled when installing applications outside Google Play.
A suspicious instruction may say:
“Play Protect detects the app, so switch it off before installation.”
Do not automatically follow it.
A warning can occasionally require further investigation, but disabling device protection is not a verification method.
Searches for a Google Play Protect bypass are also commonly exploited by sites distributing modified APK files.
SHA-256 Checksum & APK Signature Verification
Cryptographic checks are more useful than visual comparisons because they examine the actual file.
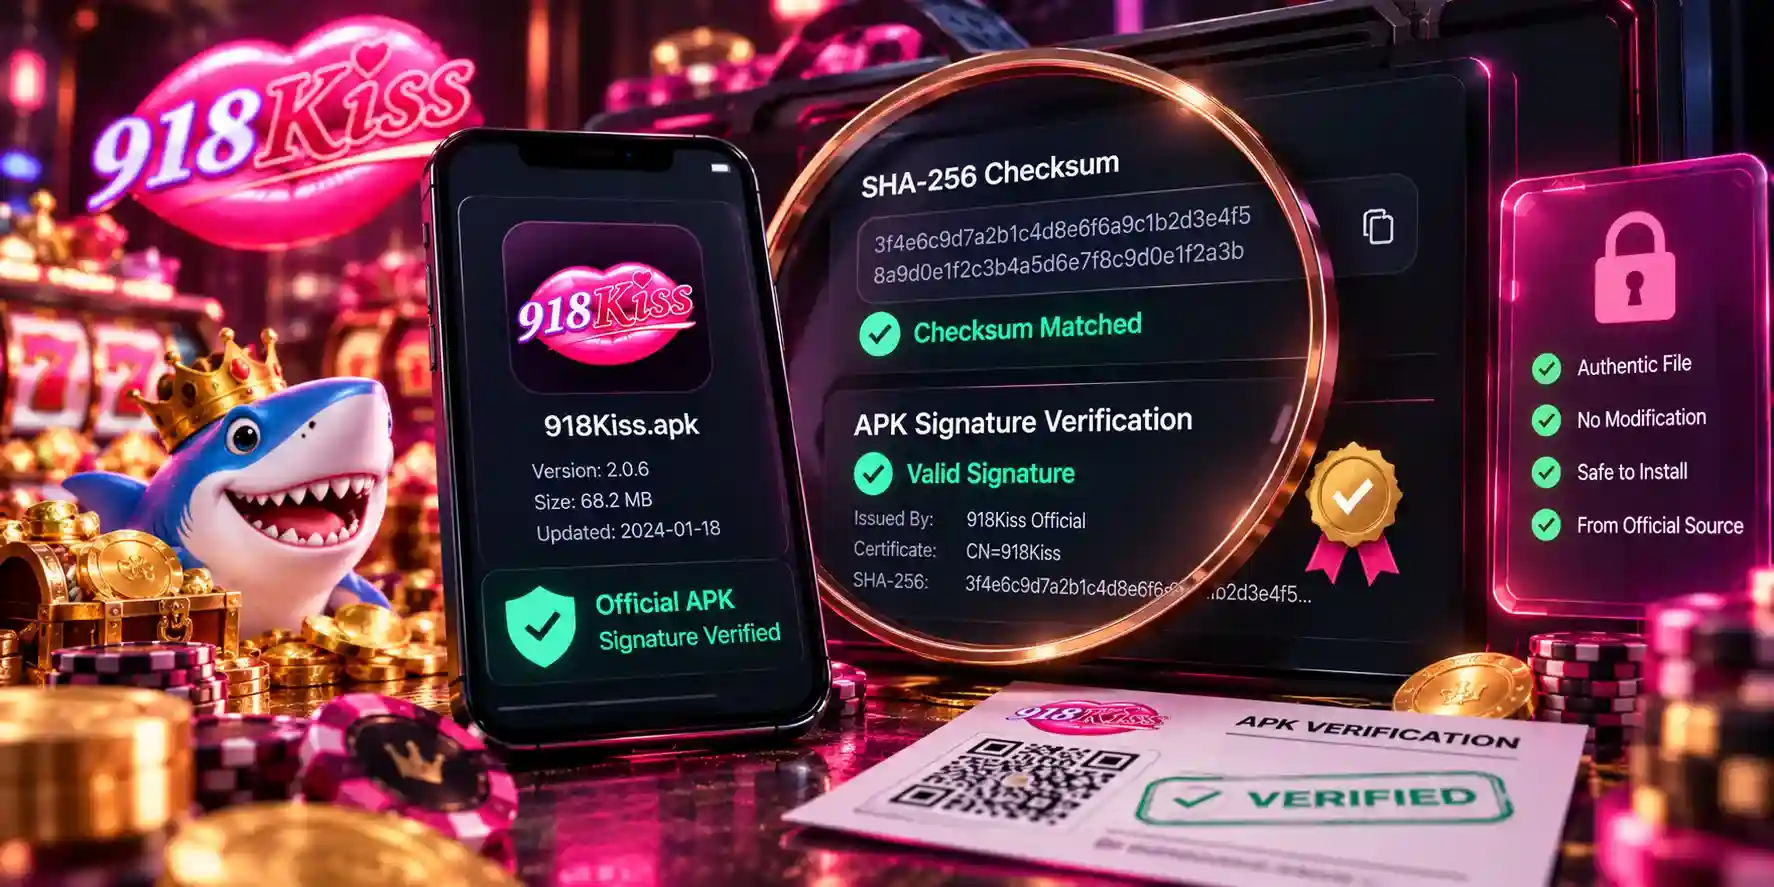
How SHA-256 Verification Works
SHA-256 generates a 64-character hexadecimal fingerprint for a file.
Example format:
EXAMPLE ONLY — NOT A KISS918 CHECKSUM

e3b0c44298fc1c149afbf4c8996fb924
27ae41e4649b934ca495991b7852b855
A real SHA-256 value normally appears as one continuous 64-character string.
If even one byte inside an APK changes, its SHA-256 hash will also change.
Check SHA-256 on Windows
Get-FileHash .\918kiss.apk -Algorithm SHA256Check SHA-256 on macOS
shasum -a 256 918kiss.apkCheck SHA-256 on Linux
sha256sum 918kiss.apkCompare the complete output against the checksum published for the exact same APK version.
Important: kiss918.games should only publish a reference SHA-256 after the specific release has been independently checked. We do not use a permanent “universal” checksum because every genuine application update changes the file and therefore changes its hash.
A proper verification entry should contain:
| Verification Data | Why It Matters |
|---|---|
| Version number | Identifies the exact release |
| File size | Basic consistency check |
| SHA-256 | Detects file modification |
| Verification date | Shows freshness |
| Source | Establishes provenance |
| Signing certificate | Helps identify the developer key |
Why a Matching SHA-256 Is Not Enough
A checksum only proves that two files are identical.
If an attacker controls both:
- the malicious APK; and
- the webpage publishing its hash,
the hash will still match.
For stronger protection, combine checksum comparison with APK signature verification and source verification.
APK Signature Verification
Android applications are digitally signed.
Users with Android SDK Build Tools can inspect the certificate using:
apksigner verify --print-certs 918kiss.apkA sudden change in the signing-certificate fingerprint between a previously trusted version and an alleged update deserves investigation.
This does not automatically prove malware, but APK signature verification provides a much stronger signal than the filename or icon.
iPhone Security: Enterprise Certificates & Configuration Profiles
iOS users do not install APK files, but they can still encounter unsafe distribution methods.
Be cautious when a website or private agent asks you to install:
- an enterprise certificate;
- a configuration profile;
- mobile device management (MDM);
- an unknown Safari profile.
Check:
Settings → General → VPN & Device Management
Review the organisation or developer name before trusting anything.
Never install an unknown configuration profile simply because somebody claims it is needed to “activate VIP”, fix a withdrawal or unlock an account.
For standard iPhone installation information, see our Kiss918 app guide.
How to Identify a Fake Kiss918 Login or Phishing Page
A phishing landing page may closely copy the original layout while sending usernames and passwords to another server.
Before entering account information, inspect the full hostname in the address bar.
This website uses:
kiss918.games
Be cautious with:
- extra words;
- additional hyphens;
- misspellings;
- unusual domain extensions;
- misleading subdomains.
For example:
kiss918.games.example.com
is a subdomain controlled by example.com — not by kiss918.games.
HTTPS is not proof of legitimacy.
HTTPS means the connection is encrypted. Phishing websites can also obtain valid TLS certificates.
Banking & E-Wallet Security
Never enter private banking credentials directly into an unknown gaming application or send them to an agent through chat.
Do not disclose:
- online banking passwords;
- ATM or debit-card PINs;
- Touch ‘n Go eWallet PINs;
- OTP or TAC codes;
- recovery codes;
- full card security information.
Payment authentication should normally take place through the bank or payment provider’s own trusted interface.
For deposit and withdrawal information, visit our payments guide.
5 Red Flags of a Fake App or Scam Agent
Use these checks before installing software or making a transfer.
1. Guaranteed Wins or RTP Manipulation
Claims involving:
- guaranteed jackpots;
- RTP hacks;
- AI prediction software;
- “admin algorithms”;
- 100% winning bots
should be treated as high-risk marketing.
A third-party bot cannot credibly guarantee the result of the next slot round.
For information about RTP and individual titles, see our games guide.
2. APK Sent Through an Unsolicited Message
A download arriving through Telegram, TikTok, WhatsApp or Messenger has no trusted chain of custody simply because the sender displays the platform logo.
3. Excessive Android Permissions
SMS, contacts, Accessibility Services, overlays and Device Administrator privileges are powerful capabilities.
Do not grant them without a clear and verifiable reason.
4. Unexpected Payment Account Changes
Stop and verify if an agent says:
“The previous account is full — send the money here instead.”
or:
“You need another deposit before your withdrawal can be released.”
Urgency is a common social-engineering technique.
5. Instructions to Disable Device Protection
Warnings include:
- disable Play Protect;
- ignore malware detection;
- enable unknown Accessibility services;
- install an unexplained iOS profile;
- give remote-control access to the device.
A safe download 918kiss process should add verification steps, not remove security controls.
Kiss918 Hack Bot Scam: Why Prediction Tools Are a Red Flag
A typical Kiss918 hack bot scam claims that software can analyse upcoming slot results or access a hidden RTP algorithm.
The user is then asked to:
- pay for the bot;
- deposit through a specific agent;
- install another APK;
- enter account credentials.
The attacker does not need working prediction software. The scam succeeds as soon as the victim sends money or installs the malicious package.
Claims such as “98% prediction accuracy” or “private server access” should therefore be treated as unverified unless backed by independently reproducible technical evidence.
What to Do After Installing a Suspicious APK
If you believe you installed a malware slot app, act before using banking or e-wallet services again.
- Stop opening the suspicious application.
- Remove any permissions you granted.
- Check Android Accessibility Services.
- Check Device Administrator and notification access.
- Check “Display over other apps”.
- Uninstall the suspicious package.
- Run Google Play Protect or your device security scanner.
- Change exposed passwords using another trusted device.
- Review bank and e-wallet transactions.
If financial credentials or OTP notifications may have been exposed, contact your bank or payment provider immediately.
For users in Malaysia who have already lost money to a scam, the National Scam Response Centre (NSRC) can be reached at 997.
Do not make an additional payment because somebody promises it will “unlock”, refund or recover the first transfer.
Report a Scam or Suspicious APK
Have you found a suspicious Telegram account, WhatsApp agent, phishing page or unknown APK?
You can report it to our security team.
Or email:
Please include where possible:
- suspicious URL;
- screenshot;
- Telegram or WhatsApp username;
- APK filename;
- file size;
- SHA-256 checksum;
- date encountered;
- short explanation of what happened.
Never send passwords, OTP/TAC codes, banking PINs, e-wallet PINs, recovery codes or full payment-card information.
If you downloaded a suspicious APK, you do not need to reopen it simply to collect evidence.
How We Review Scam Reports
We do not classify an app, website or individual as fraudulent solely because of one anonymous complaint.
Where possible, we compare technical and behavioural indicators such as:
- SHA-256 fingerprints;
- Android Manifest permissions;
- APK signing certificates;
- redirect chains;
- suspicious domains;
- screenshots;
- repeated independent reports;
- known malware behaviour.
Reports supported by multiple independent signals carry more weight than screenshots or accusations without context.
For platform-level trust analysis rather than malware verification, see our Kiss918 review.
Quick Security Checklist
Before installing an app or sending a payment, confirm:
- The download came from a source I intentionally selected.
- The file size is consistent with the expected release.
- I understand that file size alone does not prove safety.
- The SHA-256 matches the correct version, if a verified reference is available.
- Android permissions are reasonable.
- No unexplained Accessibility access is requested.
- Google Play Protect remains enabled.
- Nobody has promised guaranteed wins or an RTP hack.
- Nobody has asked for my banking PIN, OTP or e-wallet PIN.
- Payment details have not changed unexpectedly.
If one or more checks fail, stop and verify before proceeding.